Your MCP Server Must Refuse That Token
· 15 min read

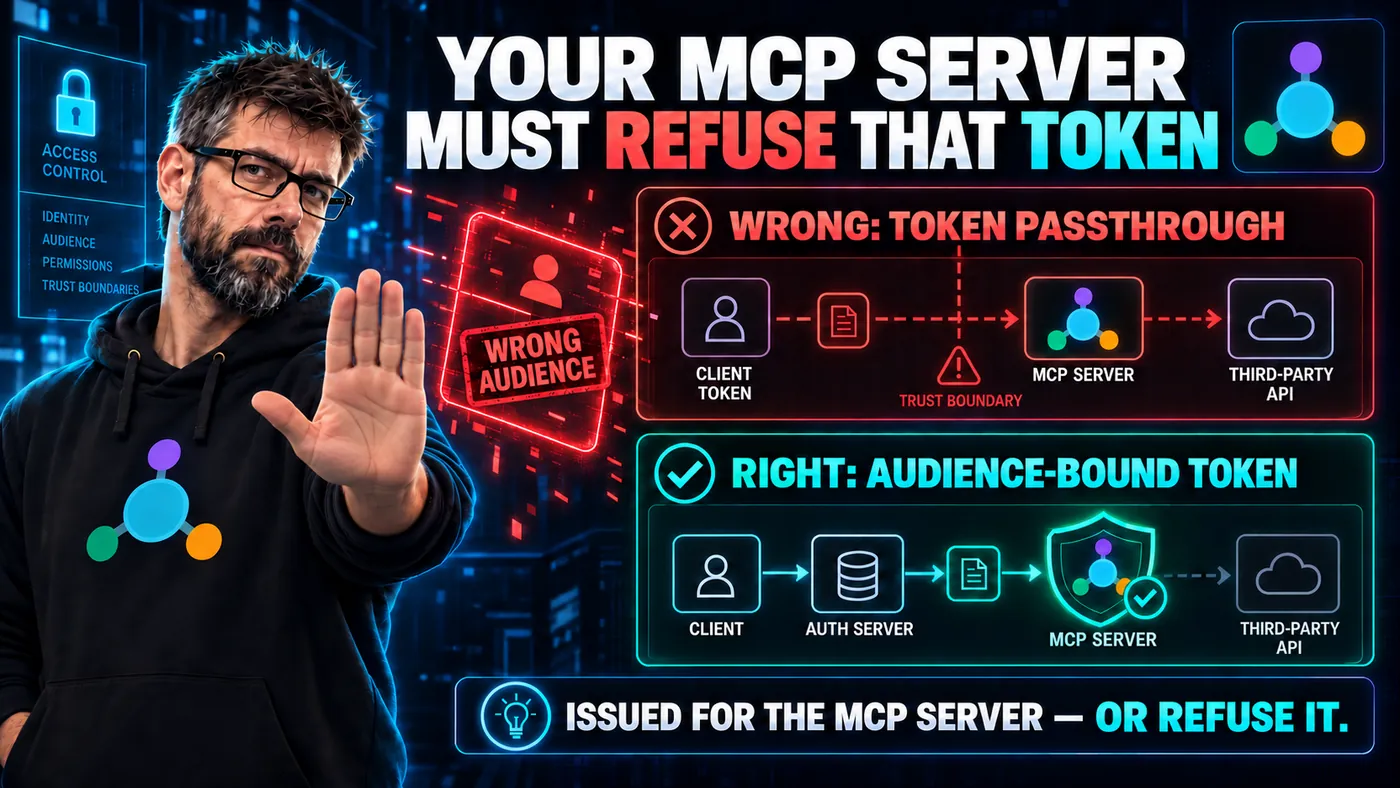
You are wrapping a third-party API in an MCP server. The client that connects to you already holds an access token for that API, and it sends the token along. Your server has the token, the API wants the token, and there is a perfectly good Authorization header sitting right there.
Forward it. Ship it. Move on.
The MCP specification states it as a hard requirement: MCP servers MUST NOT accept any tokens that were not explicitly issued for the MCP server. It is worth understanding why the bar is set there.